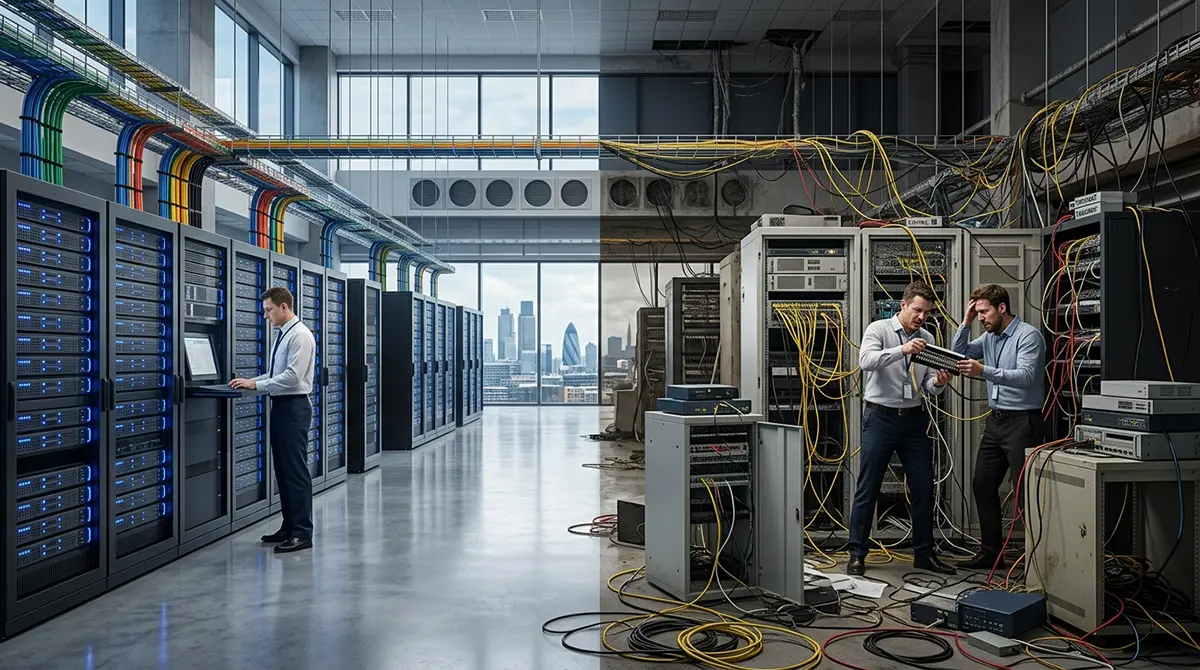



In the modern enterprise landscape, digital infrastructure is the nervous system of daily operations. When designed with consistency, discipline, and architectural clarity, an information technology environment acts as a seamless engine for innovation, scalability, and resilience. However, as organizations grow through rapid expansion, mergers, acquisitions, or decentralized decision-making, their technological foundations often fragment. What emerges is a non-standardized IT environment, a chaotic mosaic of legacy software, disparate operating systems, shadow cloud deployments, unmanaged mobile devices, and ad-hoc hardware configurations.
While decentralization is sometimes defended in the name of speed or departmental autonomy, the reality from a cybersecurity perspective is stark. Non-standardized environments create pervasive, structural security risks that compromise visibility, erode compliance, amplify operational complexity, and hand malicious actors a massive, unpredictable attack surface. Understanding these risks is not merely a technical exercise; it is an executive imperative for safeguarding organizational survival.
The Fragmented Frontier: Understanding the Anatomy of Non-Standardization
To address the security vulnerabilities of a non-standardized IT environment, one must first recognize how non-standardization manifests across an enterprise. It rarely happens overnight. Instead, it creeps in through gradual technological drift.
Consider a mid-sized enterprise where different departments possess the autonomy to select their own software, hardware, and operational protocols. The marketing department adopts a third-party Cloud SaaS platform without notifying security teams. The engineering division deploys custom Linux distributions tailored to niche development preferences. Finance relies on legacy on-premises servers running outdated Windows Server builds, while human resources uses an off-the-shelf HR portal with separate identity structures.
This technological sprawl produces a fragmented digital ecosystem. Key characteristics of a non-standardized IT ecosystem include:
-
Heterogeneous Operating Systems and Builds: Multiple releases, distributions, and patch levels of Windows, macOS, and Linux running concurrently without centralized image management.
-
Inconsistent Identity and Access Management (IAM): Fragmented directory services, decentralized user stores, and varying authentication standards across cloud and on-premises applications.
-
Uncoordinated Security Tools: A mix of antivirus software, endpoint detection and response (EDR) agents, and firewalls sourced from multiple vendors with minimal central orchestration.
-
Shadow IT and Unmanaged Assets: Unapproved cloud applications, personal devices, and unauthorized network equipment operating beyond the view of central IT operations.
-
Diverse Network Architectures: Disparate network configurations, inconsistent firewall rule sets, and varied VPN or zero-trust implementations across regional offices.
When an organization operates in this state, cybersecurity shifts from a proactive, risk-managed discipline to a reactive game of whack-a-mole. Every unique system, unapproved tool, or custom configuration introduces an isolated set of assumptions, configurations, and vulnerabilities.
The Blind Spot Dilemma: How Lack of Visibility Destroys Defense
A fundamental axiom of cybersecurity is simple: you cannot secure what you cannot see. High visibility across all endpoints, networks, cloud environments, and user activities is the prerequisite for effective threat detection and response. Non-standardized IT environments inherently destroy this visibility, creating vast digital blind spots where threats can dwell undetected for months.
When systems are uniform, security teams can implement centralized telemetry, deploying unified log collectors, standardized EDR agents, and automated Security Information and Event Management (SIEM) pipelines. Every node speaks the same operational language and logs events according to predictable schemas.
In a non-standardized environment, this streamlined monitoring collapses:
-
Incompatible Log Formats: Different operating systems, proprietary appliances, and custom applications format event logs in wildly divergent ways. Ingesting, parsing, and normalizing this chaotic data into a central SIEM requires extensive, error-prone manual labor.
-
Agent Fatigue and Blind Endpoints: Security agents designed for one operating system version may not run on another. As a result, older or non-standard machines often remain completely unmonitored because security software cannot be deployed to them.
-
Fragmented Threat Hunting: Threat hunters rely on consistent behavioral baselines to spot anomalies. When every workstation, server, and cloud bucket is configured differently, defining what constitutes normal behavior becomes nearly impossible. Abnormal malicious activity seamlessly blends into the background noise of environment-wide inconsistency.
Attackers thrive in these blind spots. Advanced Persistent Threat (APT) groups actively seek out unmonitored, non-standard endpoints as initial entry points because they know security operations center (SOC) analysts will receive no alerts when those devices are compromised.
Patch Management Paralysis: The Exposure Gap
Flawless vulnerability management relies on predictability, automation, and repeatable testing. In a standardized environment, software updates and security patches are tested against a single golden image before being pushed out en masse via automated deployment pipelines. If the patch functions correctly on the standard build, administrators can be confident it will not disrupt operations across thousands of identical machines.
Non-standardization brings patch management to a virtual standstill, dramatically widening the exposure window between the disclosure of a vulnerability and its remediation.
If you frequently encounter such security errors or unauthorized intrusions on your servers, check out our “IT support services in UAE” page for a professional infrastructure audit.
The Complexity of Compatibility Testing
When an environment contains dozens of different hardware builds, driver combinations, and operating system builds, a vendor-issued security patch cannot be deployed blindly. A update that fixes a critical zero-day vulnerability might break a legacy line-of-business application running on an unstandardized server build. Fearful of causing operational downtime, IT managers delay patch deployment to conduct endless manual compatibility testing across every unique combination of systems.
Inconsistent Update Mechanisms
Without standardized software deployment tools, updates must be orchestrated through multiple disparate channels. Some systems receive automatic cloud updates, others require manual administrative intervention, and older systems may be completely abandoned by their manufacturers.
Vulnerability Tracking Failure
In a sprawling, non-standard ecosystem, security teams struggle to maintain an accurate Software Bill of Materials (SBOM) or asset inventory. Knowing that a critical vulnerability exists in a specific library is useless if the security team cannot reliably determine which non-standard machines utilize that library.
This patch management paralysis gives cybercriminals a massive advantage. While security teams struggle with compatibility testing and system identification, threat actors use automated scanners to locate unpatched, non-standard devices connected to the enterprise network.
Configuration Drift and the Expansion of the Attack Surface
Configuration management is the discipline of maintaining hardware and software in a known, secure state. Standardized environments use infrastructure-as-code (IaC), group policies, and configuration management tools to enforce secure baselines, such as hardening guidelines from the Center for Internet Security (CIS).
In non-standardized environments, configuration drift becomes permanent. Every system administrator, departmental lead, or remote employee modifies their systems based on personal preference or immediate convenience, introducing dangerous configuration flaws across the network.
Key security vulnerabilities born from configuration drift include:
-
Default Credentials and Permissive Settings: Unstandardized equipment often retains factory default passwords, exposed management interfaces, and unnecessarily permissive file access permissions.
-
Unnecessary Services and Open Ports: Standardized images disable unused protocols, open ports, and system services by default. Non-standardized setups routinely leave services like SSH, RDP, or SMB exposed to internal or external networks without justification.
-
Inconsistent Encryption Protocols: While standard systems enforce strong transport layer security (TLS 1.3) and full-disk encryption, non-standardized assets may use deprecated protocol versions or lack disk encryption entirely.
-
Misconfigured Cloud Resources: Shadow IT and unstandardized cloud adoption lead to publicly accessible S3 buckets, permissive Identity and Access Management (IAM) policies, and unencrypted databases deployed without centralized oversight.
Every non-standard system represents a custom configuration puzzle. For an attacker, identifying just one misconfigured, non-standard node is often enough to establish a persistent foothold within the corporate perimeter.
“Don’t let cyber threats compromise your growth scale confidently with trusted website security maintenance dubai.”
The Identity Crisis: Weakened Access Control and Privilege Creep
Identity is the modern security perimeter. Whether an organization adopts a traditional defense-in-depth model or a Zero Trust architecture, controlling who has access to which resources is fundamental. Non-standardization severely undermines Identity and Access Management (IAM) policies, leading to authentication gaps and unchecked privilege creep.
When an enterprise lacks a single, standardized directory service (such as a unified Active Directory or cloud identity provider), identity governance fractures into isolated silos:
[ Decentralized User Accounts ] ---> [ Multiple Password Policies ]
                                           |
                                           v
[ Orphaned Accounts / Creep ]  <--- [ Security Gaps & Shadow Access ]
Fragmented User Accounts
Employees end up maintaining separate credentials across multiple independent systems. This leads directly to password reuse, weak passwords, and widespread resistance to security controls.
Inconsistent Multi-Factor Authentication (MFA)
While standardized systems can enforce MFA universally across all applications, legacy or non-standard systems frequently lack native support for modern authentication protocols like SAML 2.0 or OpenID Connect. These systems remain protected only by weak single-factor passwords.
Privilege Creep and Orphaned Accounts
When an employee changes roles or leaves the organization, offboarding in a non-standardized environment becomes a manual nightmare. Administrators may disable the user’s primary corporate account while forgetting local accounts on specialized Linux servers, secondary cloud portals, or legacy databases. These orphaned accounts become prime targets for malicious actors seeking persistent access.
Excessive Administrative Privileges
To bypass software incompatibilities on non-standard workstations, IT helpdesks frequently grant end users local administrative rights. This dangerous practice ensures that if an endpoint is infected with malware, the payload executes with high privileges, enabling lateral movement and ransomware deployment across the wider network.
Operational Friction and SOC Burnout: The Human Cost
The consequences of non-standardization extend beyond system vulnerabilities; they heavily impact the human professionals responsible for defending the enterprise. Security Operations Center (SOC) analysts, incident responders, and IT administrators bear the brunt of operational complexity.
In a standardized organization, security teams develop deep familiarity with a predictable set of tools, workflows, and system behaviors. Troubleshooting is structured, incident response playbooks are clear, and automation can handle routine alerts.
In a non-standard environment, operational friction dominates daily security work:
-
Playbook Breakdown: Incident response playbooks assume a degree of predictability. When an analyst responds to a breach on a non-standard server running a custom OS build, standard remediation scripts fail, requiring slow, manual, high-stakes troubleshooting during an active crisis.
-
Alert Fatigue and False Positives: Disparate tools and erratic system behaviors generate massive volumes of noisy, conflicting alerts. SOC analysts spend countless hours investigating false positives triggered by benign variations in non-standard software, leading to cognitive fatigue and missed real alerts.
-
Skills Fragmentation: Security staff must become jacks-of-all-trades, expected to understand dozens of operating system versions, security vendors, and hardware platforms. Depth of security expertise is sacrificed for broad, surface-level maintenance across an unmanageable stack.
-
Ineffective Automation: Modern security relies on Security Orchestration, Automation, and Response (SOAR) platforms to isolate infected endpoints, revoke compromised credentials, and block malicious IPs automatically. Automation requires standardized APIs and consistent environments; in non-standard settings, automated playbooks break down constantly.
When security staff are consumed by the friction of managing chaos, they lose the capacity to perform proactive threat hunting, strategic risk planning, and architectural improvement.
Regulatory Non-Compliance and Audit Failure
Compliance frameworks such as ISO/IEC 27001, SOC 2, NIST SP 800-53, HIPAA, PCI-DSS, and GDPR are designed to ensure that organizations maintain robust, verifiable control over sensitive data. Central to every compliance standard is the requirement for consistent administrative, technical, and physical safeguards.
Non-standardized IT environments present an immediate threat to regulatory compliance and audit readiness:
-
Inability to Demonstrate Control: Auditors demand evidence that security policies apply uniformly across all assets within scope. Providing consistent evidence from a fragmented network of custom builds, unmanaged cloud tenants, and varying security agents is nearly impossible.
-
Data Sprawl and Loss of Governance: Non-standard systems and shadow IT lead to unmonitored data replication. Sensitive customer information, protected health information (PHI), or payment data spreads across unencrypted, non-standard drives and unauthorized cloud storage, directly violating privacy regulations like GDPR and HIPAA.
-
Failed Access Reviews: Regulatory standards mandate regular access certifications to ensure the principle of least privilege. In non-standard environments with fragmented user directories, comprehensive access reviews become inaccurate, leading to severe audit findings.
Failing an audit is not just an administrative inconvenience. It brings catastrophic financial penalties, legal liabilities, loss of operating licenses, and severe reputational damage that can undermine customer trust for years.
Incident Response Delays and Disaster Recovery Disasters
When a ransomware attack, nation-state intrusion, or catastrophic hardware failure strikes, time is the critical variable. The speed with which an organization can detect, contain, eradicate, and recover from an incident determines the overall financial and operational damage.
Non-standardization slows every phase of incident response and undermines business continuity:
[ Detection & Containment ] ---> Slowed by varied telemetry & custom systems
                                          |
                                          v
[ Eradication & Recovery ]  ---> Complicated by mismatched backups & builds
Containment Delays
When a threat actor moves laterally through a network, containment requires isolating affected hosts immediately. In a standardized network, network access control (NAC) tools or centralized endpoint software can isolate compromised devices with a single automated command. In an unstandardized environment, disparate security tools may lack isolation capabilities, forcing security teams to physically locate or manually disconnect non-standard assets.
Forensics Complications
Digital forensics experts rely on timeline analysis, memory analysis, and log correlation to reconstruct an attack. Non-standardized log formats, missing audit logs on unmanaged devices, and inconsistent system clocks turn forensic investigations into long, uncertain puzzles.
Backup and Recovery Failures
Disaster recovery plans depend on standard, verified recovery procedures. If an enterprise relies on multiple incompatible backup tools, non-standard server configurations, and undocumented custom software builds, bare-metal recovery becomes impossible. System administrators are forced to rebuild complex servers from scratch during an active crisis, extending operational downtime from hours to weeks.
Strategic Blueprint: Transitioning from Chaos to Standardization
Overcoming the security risks of a non-standardized IT environment requires a deliberate, long-term strategic commitment from executive leadership, IT operations, and cybersecurity teams. Standardization is not about stifling departmental innovation; it is about establishing a secure, scalable platform upon which innovation can safely occur.
Organizations seeking to eliminate the risks of non-standardization should execute a multi-phased strategic transformation:
1. Execute Comprehensive Asset Discovery
Before standardizing, organizations must gain total visibility over their current holdings.
-
Deploy passive network monitoring, automated asset discovery scanners, and cloud management tools to identify every connected physical device, virtual machine, cloud resource, and software application.
-
Uncover and document all instances of shadow IT and unauthorized hardware.
2. Define and Enforce Standard Operating Environments (SOEs)
Establish a minimalist set of core technological standards across the enterprise.
-
Build standard, hardened golden images for workstations, servers, and containerized workloads based on established benchmarks like CIS or NIST.
-
Mandate centralized image deployment so that all new hardware or virtual instances instantiate exclusively from approved standards.
3. Consolidate Identity and Enforce Zero Trust
Eliminate identity silos by establishing a single source of truth for identity management.
-
Integrate all local directories, cloud applications, and legacy systems into a centralized Identity Provider (IdP).
-
Enforce universal Multi-Factor Authentication (MFA), role-based access control (RBAC), and least privilege access across all platforms.
4. Rationalize and Centralize Security Tools
Eliminate redundant, disparate security solutions in favor of an integrated security architecture.
-
Standardize on a unified Endpoint Detection and Response (EDR) solution, unified log management platform, and consolidated network security stack.
-
Ensure all security tools communicate seamlessly with a centralized SIEM and SOAR platform.
5. Standardize Procurement and Governance
Prevent technological drift from re-emerging by establishing strict governance frameworks.
-
Implement centralized procurement policies requiring security review and architecture approval for all new software, hardware, and cloud subscriptions.
-
Establish continuous monitoring tools to detect and automatically remediate configuration drift across the entire environment.
Conclusion: Standardization as a Competitive Security Advantage
In an era defined by relentless cyber threats, operational complexity is the ultimate enemy of security. A non-standardized IT environment creates an asymmetrical advantage for threat actors, forcing security teams to defend a chaotic, unpredictable landscape riddled with blind spots, patch gaps, misconfigurations, and identity silos.
Conversely, IT standardization transforms cybersecurity from a fragmented, reactive effort into a streamlined, proactive discipline. By standardizing operating systems, hardware configurations, identity stores, and security toolsets, organizations reduce their attack surface, accelerate incident response times, lower operational costs, and build a resilient foundation for long-term digital growth.
Standardization is not merely a technical cleanup initiative; it is a critical security posture. In the digital modern age, consistency is not just an operational virtue, it is the cornerstone of enterprise resilience.
Strategic Action Checklist for Security Leaders
To operationalize the transition toward a standardized, secure environment, leadership can utilize this actionable evaluation checklist:
-
Inventory Baseline: Is there an automated asset discovery tool continuously updating a real-time inventory of all hardware, software, and cloud assets across the organization?
-
Golden Image Management: Are formal Standard Operating Environments (SOEs) defined, hardened, and automatically applied to all newly deployed servers, workstations, and cloud instances?
-
Identity Consolidation: Is a single, centralized Identity Provider (IdP) used to authenticate access across all enterprise applications, infrastructure, and cloud platforms?
-
Automated Patch Management: Does the vulnerability management program achieve automated patch deployment across all operational builds within defined SLA windows?
-
Security Stack Integration: Are endpoint monitoring, log collection, and incident response tools consolidated into a single management architecture reporting to a central SIEM?
-
Governance and Procurement Controls: Are strict technical governance policies enforced to block shadow IT, unapproved software, and unhardened hardware deployment?