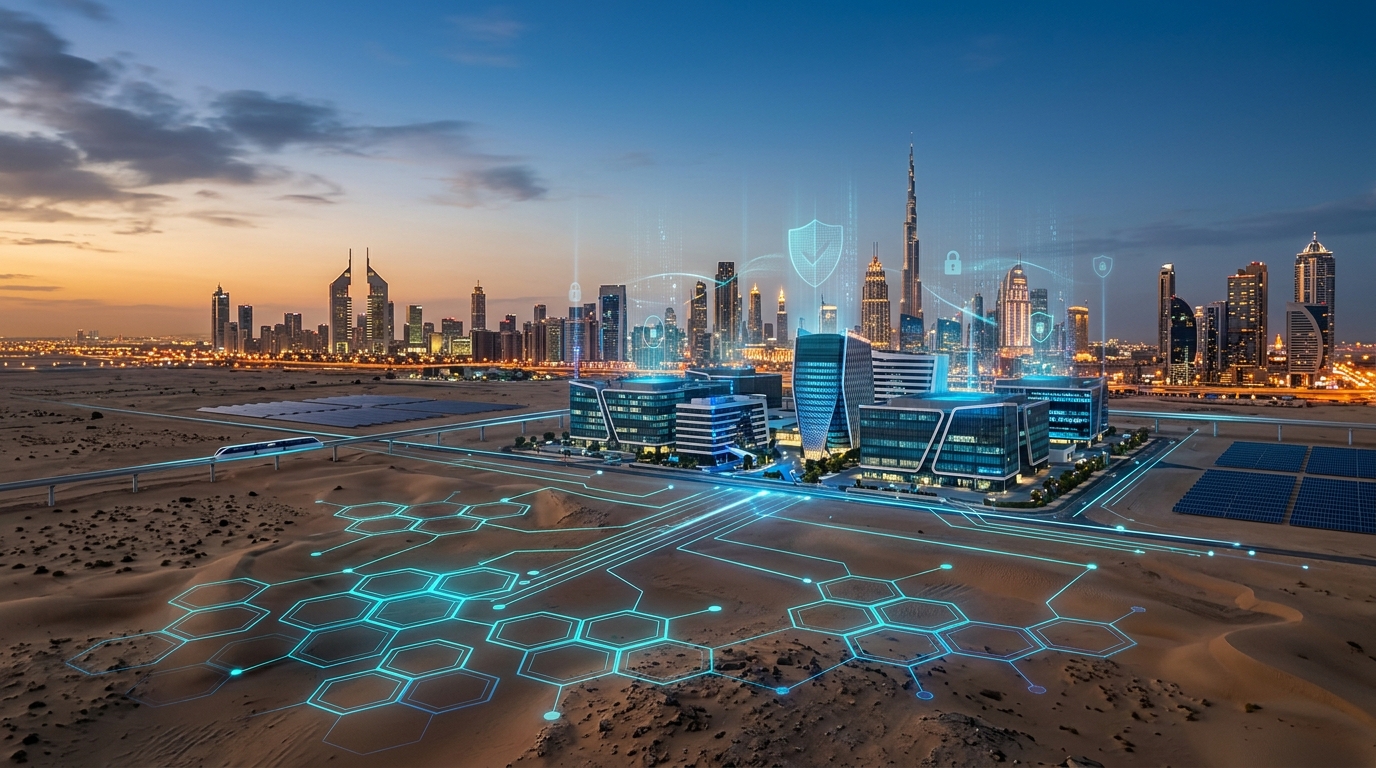
Dubai has evolved at a breathtaking pace from a regional trading hub into a global epicenter for technological innovation, artificial intelligence, and digital commerce. Under ambitious government blueprints such as the Dubai Smart City initiative and the Dubai Cyber Security Strategy, the emirate aims to create the safest cyberspace in the world. However, this relentless drive toward digital transformation has also expanded the threat landscape. As Dubai enterprises migrate workloads to hybrid cloud environments, embrace remote work, and integrate Internet of Things devices into their operational infrastructure, traditional perimeter-based security models have become fundamentally obsolete.
For decades, organizations relied on a castle-and-moat security philosophy. Once a user or device successfully authenticated at the network edge, they were implicitly trusted to move freely across internal networks. In today’s hyper-connected enterprise ecosystem, this approach is a catastrophic vulnerability. Cybercriminals no longer break in; they log in using compromised credentials, lateralize through flat networks, and exfiltrate sensitive data with impunity. To combat these sophisticated threats, the Dubai Electronic Security Center (DESC) has established rigorous regulatory mandates that urge organizations to adopt advanced defensive frameworks.
At the heart of this modern compliance paradigm lies Zero Trust Architecture (ZTA). Far more than a passing cybersecurity buzzword, Zero Trust is a strategic framework built on a singular, uncompromising principle: never trust, always verify. For enterprises operating within Dubai, aligning cybersecurity postures with Zero Trust is no longer optional. It is a critical operational imperative required to satisfy DESC compliance, protect corporate intellectual property, safeguard customer data, and maintain a competitive edge in one of the world’s most dynamic business environments.
Understanding the Regulatory Landscape: The Role of DESC
To appreciate why Zero Trust Architecture has become essential for Dubai businesses, one must first examine the regulatory body governing the emirate’s cyber domain. The Dubai Electronic Security Center was established to secure Dubai’s government networks, information systems, and critical infrastructure against rising cyber threats. Over the years, DESC’s mandate has expanded from protecting government entities to establishing baseline cybersecurity standards for all businesses, service providers, and critical national infrastructure operators within the emirate.
DESC issues comprehensive compliance frameworks that dictate how organizations must manage risk, secure data, and respond to incidents. These frameworks are designed to align with international best practices while addressing local threat vectors and strategic priorities. Compliance with DESC regulations is mandatory for entities operating within critical sectors such as finance, energy, healthcare, transportation, and government contracting. Non-compliance can result in severe financial penalties, operational shutdowns, reputational damage, and loss of business licenses.
Traditional security measures such as firewalls, virtual private networks, and basic antivirus solutions are no longer sufficient to meet DESC’s stringent audit requirements. DESC standards increasingly emphasize continuous monitoring, strict identity verification, data-centric security, and micro-segmentation. These requirements mirror the core tenets of Zero Trust Architecture. By implementing a Zero Trust framework, Dubai enterprises can build a compliance-ready security posture that satisfies DESC auditors while simultaneously fortifying their defenses against advanced persistent threats and ransomware campaigns.
Empower your enterprise with seamless connectivity explore our tailored Internal Communication Network Solutions for Businesses in Dubai.
The Core Principles of Zero Trust Architecture
Zero Trust Architecture is not a single product, software suite, or hardware appliance that an enterprise can simply purchase and install. Instead, it is a holistic security model, design philosophy, and operational framework that transforms how organizations view risk and trust. The architecture rests upon three fundamental pillars established by standard-setting bodies like the National Institute of Standards and Technology, which align seamlessly with DESC compliance objectives:
Explicit Verification: Organizations must always authenticate and authorize based on all available data points, including user identity, location, device health, service or workload context, data classification, and anomalies. Implicit trust based on network location is entirely eliminated.
Least Privilege Access: Users and devices must be granted only the minimum level of access necessary to perform their specific tasks. Access rights are bounded by Just-In-Time and Just-Enough-Access models, risk-adaptive policies, and data protection controls that limit blast radius during a security incident.
Assume Breach: Enterprises must operate with the mindset that attackers have already penetrated the perimeter. Organizations must minimize blast radius by segmenting access by network, user, devices, and application awareness. Encryption must be deployed universally across all data states, and analytics must be utilized to gain deep visibility into threat telemetry.
By operationalizing these three core principles, Dubai enterprises move away from static, perimeter defenses and toward dynamic, context-aware security policies. Every single access request, whether originating from an executive laptop inside a Downtown Dubai corporate office or a remote employee connecting from overseas, is scrutinized through real-time risk assessment engines before entry is granted.
Identity as the New Perimeter in Dubai Enterprises
In a traditional network architecture, the physical firewall served as the corporate boundary. In a modern Zero Trust environment, identity is the new perimeter. Because Dubai enterprises frequently employ multicultural, globally distributed workforces, contractors, and third-party vendors, managing human and machine identities securely is the most vital component of DESC compliance.
Identity and Access Management (IAM) under a Zero Trust model goes far beyond standard username and password combinations. Passwords are inherently weak, easily phished, and prone to credential stuffing attacks. Zero Trust mandates the implementation of robust Multi-Factor Authentication (MFA) across all enterprise applications, including cloud services, internal portals, and legacy systems. However, basic MFA is often bypassed by modern adversary-in-the-middle phishing attacks. Consequently, Dubai enterprises are transitioning toward passwordless authentication methods, such as FIDO2-compliant security keys, biometric verification, and context-aware adaptive MFA.
Furthermore, Zero Trust IAM incorporates continuous risk scoring. If an employee logs in from a standard office IP address during regular business hours, access is smoothly granted. If that same employee’s credentials attempt to log in from an anomalous geographic location at three in the morning while simultaneously trying to access sensitive financial databases, the Zero Trust policy engine automatically triggers step-up authentication, restricts access, or blocks the session entirely. This level of granular control satisfies DESC requirements for proactive identity governance and insider threat mitigation.
Device Security and Endpoint Verification
Beyond human identity, every device attempting to connect to a Dubai enterprise network represents a potential entry point for cyber threats. Corporate laptops, mobile phones, contractor tablets, and Internet of Things hardware must all undergo rigorous verification before being granted access to enterprise resources.
Under Zero Trust, unmanaged personal devices, often referred to under Bring Your Own Device policies, are treated with high suspicion. Enterprises must enforce strict Endpoint Detection and Response solutions that continuously monitor device health, operating system patch levels, anti-malware status, and configuration compliance. If a device is found to be running outdated, vulnerable software or lacking active security agents, access to corporate data is automatically quarantined until the device is remediated.
This device-centric verification is especially critical for Dubai enterprises operating in sectors like logistics, retail, and smart infrastructure, where thousands of edge devices connect to central enterprise networks. DESC compliance frameworks require comprehensive asset visibility and endpoint hardening. Zero Trust ensures that no device, regardless of ownership, is trusted blindly. Continuous posture assessment guarantees that compromised endpoints cannot serve as springboards for malware propagation or data exfiltration across the organization.
Micro-Segmentation and Network Minimization
Network architecture within Dubai enterprises has historically suffered from flat designs, where internal networks resemble open meadows. Once an attacker gained access through a phishing email or vulnerable public-facing server, they could freely roam across the network, discovering critical assets, harvesting credentials, and establishing persistence. Zero Trust Architecture systematically dismantles this vulnerability through micro-segmentation.
Micro-segmentation involves dividing the data center and cloud environments into small, isolated zones down to the workload or application level. Traffic between these segments is restricted by granular security policies enforced by software-defined networking and next-generation firewalls. If an attacker breaches a marketing department laptop, micro-segmentation ensures they remain trapped within that specific micro-perimeter, entirely cut off from financial databases, customer registries, and intellectual property repositories.
For Dubai organizations striving for DESC compliance, micro-segmentation provides verifiable proof of defense-in-depth and risk mitigation. Auditors look favorably upon architectures that limit lateral movement and enforce strict traffic controls between internal segments. By treating internal networks with the same suspicion applied to the public internet, enterprises drastically reduce their attack surface and fulfill core regulatory mandates.
Data-Centric Security and Encryption Standards
Ultimately, the primary target of cybercriminals is data. Whether dealing with proprietary artificial intelligence algorithms, customer personally identifiable information, or classified government communications, Dubai enterprises hold vast amounts of sensitive data that require absolute protection. Traditional security focused heavily on protecting networks and servers, often leaving data vulnerable once exfiltrated. Zero Trust shifts the focus toward data-centric security.
A robust Zero Trust data strategy begins with comprehensive data discovery, classification, and labeling. Enterprises must know where their sensitive data resides, whether at rest in databases, in transit across networks, or in use by applications. Once classified, data must be protected using strong encryption standards both at rest and in transit. Furthermore, rights management solutions should be implemented to ensure that data remains encrypted and protected even if it leaves the physical or logical boundaries of the enterprise network.
DESC regulations place heavy emphasis on data privacy, sovereignty, and protection. With regulations like the UAE Data Protection Law and DESC guidelines working in tandem, enterprises face severe legal consequences if sensitive data is compromised. Zero Trust ensures that data access is tied directly to user authorization and contextual risk, rendering stolen data useless to unauthorized actors because it remains heavily encrypted and locked behind strict cryptographic keys.
Application Security and Workload Protection
Modern applications developed by Dubai enterprises are increasingly complex, built on microservices architectures, containerized using platforms like Kubernetes, and deployed across multi-cloud environments spanning local data centers and hyperscalers such as Microsoft Azure, Amazon Web Services, and Google Cloud. Securing these dynamic application workloads requires a modern approach that traditional perimeter defenses cannot provide.
Zero Trust application security mandates that workloads verify each other continuously. Service-to-service communication within container clusters must be authenticated and encrypted using mutual TLS. Furthermore, application security must be integrated into the development lifecycle through DevSecOps practices, ensuring that code is scanned for vulnerabilities, misconfigurations, and hardcoded credentials before deployment into production environments.
For enterprises regulated by DESC, securing cloud workloads is a frequent audit focus. Regulatory frameworks require visibility into all cloud assets and proof that cloud configurations comply with security benchmarks. Zero Trust posture management tools continuously scan cloud environments for compliance drift, ensuring that accidental public cloud storage buckets or misconfigured IAM roles are identified and remediated before malicious actors can exploit them.
Overcoming Implementation Challenges in Dubai Enterprises
Transitioning an established enterprise toward a Zero Trust Architecture is a transformative journey that comes with significant operational, technical, and cultural challenges. Business leaders in Dubai must navigate several common hurdles when aligning their organizations with DESC compliance standards through Zero Trust.
One primary challenge is legacy infrastructure compatibility. Many established enterprises in Dubai still rely on legacy monolithic applications and aging hardware that do not natively support modern identity federation, API integration, or micro-segmentation. Rip-and-replace strategies are often financially prohibitive and operationally disruptive. Organizations must adopt a phased migration approach, utilizing intelligent proxies, identity gateways, and micro-perimeters to wrap legacy systems in Zero Trust controls while modernizing applications over time.
Another challenge is cultural resistance and user friction. Employees accustomed to frictionless internal network access may initially push back against multi-factor authentication prompts, device checks, and restricted access permissions. Overcoming this requires robust internal communication, executive sponsorship, and user-centric security design that minimizes unnecessary friction while maximizing protection. Security teams must position Zero Trust not as a bureaucratic roadblock, but as an enabler of secure digital business innovation.
Finally, skill shortages in advanced cybersecurity disciplines remain a global issue that impacts Dubai enterprises. Implementing and managing a complex Zero Trust ecosystem requires specialized expertise in identity engineering, cloud security architecture, and automated threat analytics. Organizations must invest heavily in upskilling existing IT personnel, partnering with reputable managed security service providers based in the UAE, and leveraging automation and artificial intelligence to bridge talent gaps.
The Business Value of DESC Compliance and Zero Trust
While achieving compliance with DESC regulations and implementing Zero Trust Architecture requires upfront capital investment, strategic planning, and cultural adaptation, the return on investment extends far beyond regulatory avoidance. Forward-thinking Dubai enterprises view cybersecurity not as a cost center, but as a core business enabler and a differentiator in the marketplace.
First and foremost, a mature Zero Trust posture dramatically reduces the likelihood and potential impact of a catastrophic cyber incident. By limiting blast radius, enforcing least privilege, and verifying every transaction, organizations can thwart ransomware attacks, insider threats, and advanced persistent threats before they disrupt business operations. This resilience protects corporate reputation, maintains customer trust, and preserves brand equity in a hyper-competitive regional market.
Furthermore, compliance with DESC standards opens doors to lucrative government contracts, strategic partnerships, and international business opportunities. Public sector entities and critical infrastructure operators in Dubai strictly require third-party vendors and suppliers to demonstrate robust cybersecurity compliance. By achieving certification and alignment with DESC guidelines through Zero Trust, enterprises position themselves as trusted, secure partners capable of participating in high-value government and enterprise projects.
Conclusion: Charting the Path Forward for Dubai Enterprises
The digital future of Dubai is extraordinarily bright, underpinned by visionary leadership, rapid technological adoption, and an unwavering commitment to innovation. However, this future can only be secured if the underlying digital infrastructure is resilient against an evolving and determined threat landscape. Traditional security models are no longer fit for purpose in a world of cloud computing, remote work, and sophisticated cybercriminal syndicates.
Zero Trust Architecture represents the gold standard in modern cybersecurity defense. By embracing the core principles of explicit verification, least privilege access, and assumed breach, Dubai enterprises can build resilient digital fortresses that satisfy the rigorous compliance mandates of the Dubai Electronic Security Center. Whether securing human identities, hardening endpoint devices, micro-segmenting internal networks, or protecting sensitive data workloads, Zero Trust provides a clear, actionable roadmap for sustainable digital security.